Key Takeaways
- AI, automation, connected equipment, and third-party systems are expanding manufacturing capabilities and the potential operational impact of a cyber incident.
- Cybersecurity has become a barrier to technology progress, making cyber resilience a business priority rather than solely an IT responsibility.
- Manufacturers should direct cybersecurity investment toward identity, OT security, third-party oversight, incident response, and operational continuity.
Manufacturers are adopting AI, expanding automation, and connecting more systems than ever before. These technologies can improve productivity and drive growth, but they also create new entry points for attackers and increase the operational consequences of a breach.
Greater spending alone does not create resilience. Manufacturers must direct investment toward the identities, operational technology, third parties, and response capabilities most critical to keeping production running.
Cybersecurity Investment is Rising with Digital Exposure
Cyber risk has become a significant challenge for mid-market manufacturers. Over 40% noted it as a top concern for growth in our 2027 Mid-Market Manufacturing Outlook, up 20 percentage points from 2026’s report. In addition, 43% of respondents cited cybersecurity concerns as a barrier to achieving their technology goals.
This aligns with other research showing cybercrime continuing to rise across industries. The rise of AI is a significant contributor, with CrowdStrike research reporting an 89% increase in attacks by AI-enabled adversaries.
For manufacturers, the risk is even more relevant. System integration and legacy equipment rank as top barriers to achieving technology goals. Interconnected systems, unsecured technology, and complex supply-chain dependencies can further increase manufacturing vulnerabilities.
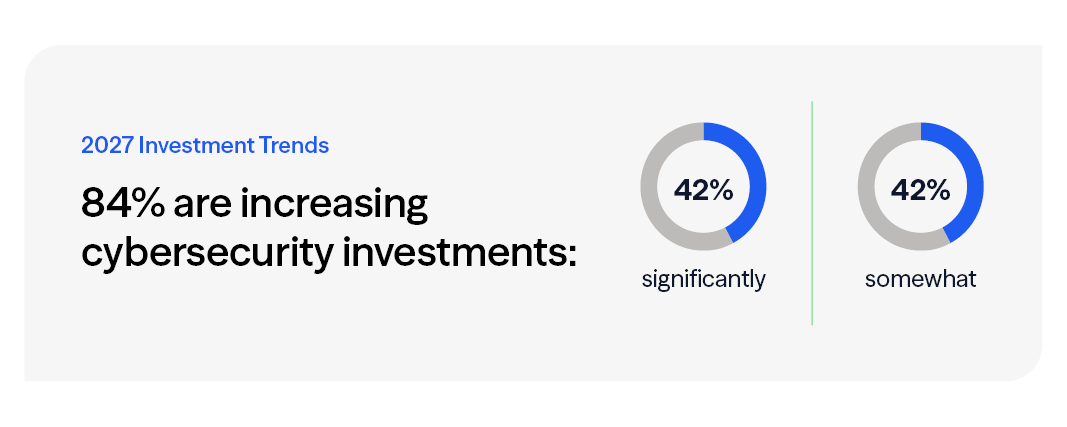
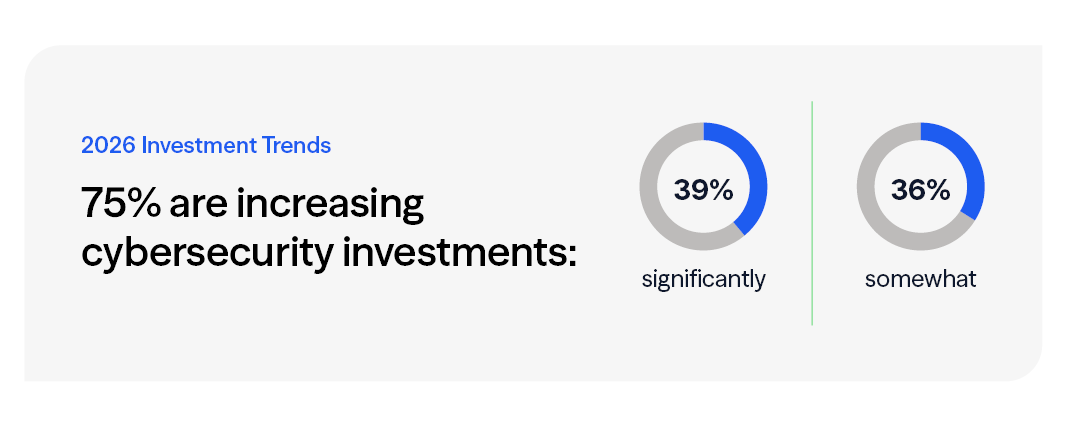
Fortunately, middle-market manufacturing leaders are taking the new threat landscape seriously. More than 80% of respondents are either significantly or somewhat increasing their cybersecurity investments, up from 75% in 2026.
Build Cyber Resilience Across the Manufacturing Environment
Manufacturers need a layered approach that protects users, IT systems, operational technology, third parties, and critical processes. Four areas deserve immediate leadership attention.
- Dive Deeper: Learn more about how to protect your manufacturing organization. Download the Proactive Playbook.
Control Access
Manufacturers must manage access across employees, contractors, vendors, service accounts, devices, machines, and applications. A Zero Trust approach requires users and systems to verify their identities and limits access according to business need.
Priority controls include:
- Multifactor authentication for all systems
- Least-privilege access for users and applications
- Separate controls for privileged and administrative accounts
- Network segmentation between IT and OT environments
- Monitoring for unusual login and access activity
These controls can limit how far an attacker moves if credentials, endpoints, or connected devices are compromised.
Strengthen Operational Technology (OT) Security
Operational technology presents a distinct challenge because many manufacturing environments depend on legacy equipment, specialized applications, and systems that cannot be patched or replaced without affecting production. Cyber incidents in this environment can create consequences beyond data loss, including downtime, safety concerns, quality disruptions, and missed customer commitments.
Manufacturers should:
- Establish an inventory of connected OT assets
- Segment critical production environments
- Monitor traffic between IT and OT systems
- Assess remote and third-party access
- Prioritize legacy assets according to operational criticality
- Develop response and recovery procedures that account for production dependencies
Utilize AI
AI can help threat actors create convincing phishing messages, accelerate reconnaissance, and automate parts of an attack. It can also help manufacturers analyze activity, identify anomalies, prioritize alerts, and respond more quickly.
Before introducing AI into security operations, manufacturers should define:
- Which systems and data the technology can access
- Who reviews AI-generated alerts and recommendations
- How outputs will be validated
- Which responses may be automated
- When human approval is required
- How vendor models and tools will be monitored
AI can improve detection and response, but it should strengthen an established security program rather than compensate for missing controls.
Manage Risk Across Supply Chain
The 2027 report also suggests that broader supplier-risk practices remain inconsistent. Only 28% of respondents reported increasing scenario planning and risk management within their supply chains, while 17% tightened supplier audits and selection criteria.
These findings suggest that supplier-risk practices may not be developing as quickly as manufacturing connectivity and digital dependence.
Because supply chains are deeply interconnected, a single vendor with weak controls can expose your entire operation. Create strong third-party oversight by:
- Identifying suppliers with access to critical systems or data
- Defining cybersecurity requirements in contracts
- Reviewing vendor access periodically
- Establishing notification and response expectations
- Evaluating concentration and operational dependency
- Including critical vendors in incident exercises
Protect Your Manufacturing Organization from Operational Disruption
Manufacturing cyber resilience depends on more than preventing an attack. Leaders must understand how an incident could affect production, safety, logistics, customer commitments, financial processes, and communication.
Incident response and business continuity plans should identify:
- Critical production systems and recovery priorities.
- Dependencies between IT, OT, vendors, and facilities.
- Alternative processes for maintaining essential operations.
- Roles and escalation paths across technology, operations, finance, legal, and executive leadership.
- Communication procedures for employees, customers, regulators, insurers, and suppliers.
- Recovery time and recovery point objectives.
Tabletop exercises should test realistic manufacturing scenarios, such as ransomware affecting production scheduling, compromised vendor access, or an OT outage halting a critical line. Testing helps leaders determine whether documented plans will work when technology, people, and production are under pressure.
Make Cybersecurity an Enabler of Manufacturing Growth
Manufacturers cannot separate digital growth from cyber risk. AI, connected equipment, supplier integration, and automation all create value by allowing information and processes to move more freely. That same connectivity can expand exposure when security, governance, and recovery capabilities fail to keep pace.
The most proactive manufacturers will be those who unify their approach to cybersecurity governance (and have leadership buy-in), enforce necessary principles for security and identity of humans and machines, and focus on operational continuity, not just IT impacts.
Cyber resilience is not measured only by whether an attack is prevented. It is measured by how quickly the organization identifies an incident, limits its impact, maintains critical operations, and recovers with confidence.
It’s time to strengthen resilience and protect growth. Download the Proactive Playbook.
Frequently Asked Questions
What is cyber resilience in manufacturing?
Cyber resilience is a manufacturer’s ability to prepare for, withstand, respond to, and recover from cyber incidents while maintaining critical operations. It includes cybersecurity controls, incident response, business continuity, OT recovery, third-party coordination, and executive decision-making.
How should manufacturers prepare for a cyber incident affecting production?
Manufacturers should identify critical systems and production dependencies, establish recovery priorities, define cross-functional roles, document alternative operating procedures, and conduct tabletop exercises. Response plans should account for both IT and OT impacts, including safety, logistics, quality, and customer commitments.
What types of cyber threats most commonly affect manufacturing organizations?
Top threats include ransomware, business email compromise, OT system intrusions, supply chain breaches, credential theft, and AI-generated phishing attacks.
How does AI increase cyber risk?
AI can help threat actors scale reconnaissance, create more convincing phishing and impersonation campaigns, automate portions of credential attacks, and adapt malicious activity more quickly. AI systems and development platforms can also become targets when they are connected to sensitive data or operational workflows without appropriate controls.
How can AI help defend against cyberattacks?
AI-enabled security tools can analyze activity, identify anomalies, prioritize alerts, and automate defined response actions. Human oversight remains essential for validating findings, investigating incidents, and determining when automated containment is appropriate.
What is Zero Trust, and why is it important for manufacturers?
Zero Trust requires verification before granting access to any system or device — crucial in environments with interconnected machinery and remote access entry points.
How can manufacturers reduce cybersecurity vulnerabilities in legacy equipment?
Manufacturers should improve visibility, segment networks, implement OT-specific security tools, and upgrade or isolate outdated devices.
Why is vendor risk management important?
A breach involving a critical supplier or service provider can affect connected systems, sensitive data, production schedules, or essential services. Manufacturers should identify high-risk vendors, define cybersecurity expectations, periodically review access, and establish incident-notification requirements.
How can manufacturers get started improving cybersecurity?
Start with a security risk assessment, evaluate OT maturity, train employees, implement Zero Trust, and address high-priority vulnerabilities.
Rely on the trusted expertise of manufacturing advisors to help you build and execute your strategic vision.
Eide Bailly’s cybersecurity team provides guidance, strategic direction, and prioritization of business objectives and cyber risks.
Who We Are
Eide Bailly is a nationally ranked accounting and advisory firm bringing financial, operational, and technical solutions to middle market and high-growth organizations.